The Accounts Outside the Policy Branch
SVP Cyber Risk
A cyber risk executive reconciles acquisition billing to an organisational policy branch and tests two accounts that the security console had omitted.
The signature device
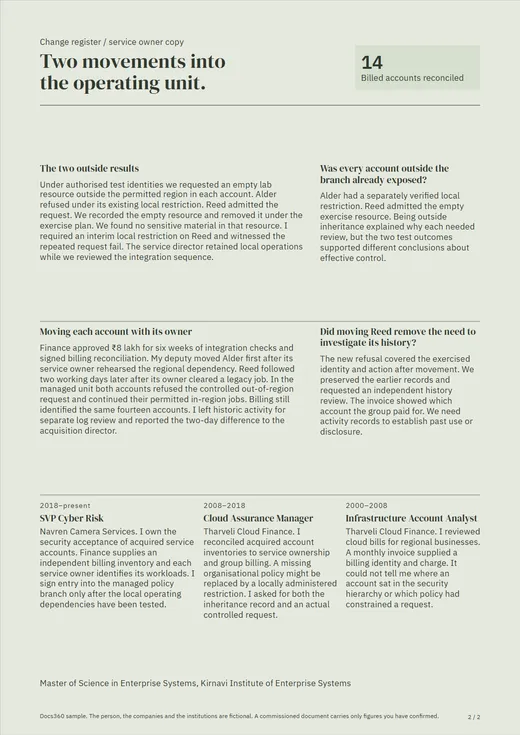
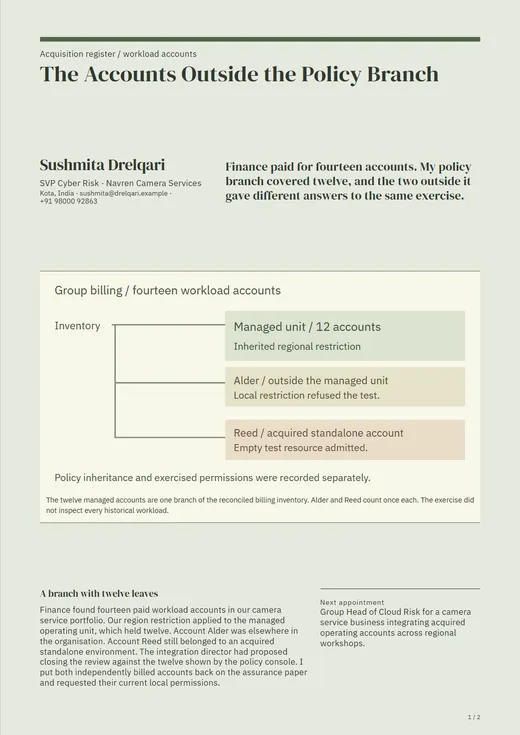
The branch drawing places twelve accounts inside the managed unit and retains both outside accounts with their separately witnessed regional control results.
Who should choose it
For an acquisition security executive who can reconcile group billing to actual policy coverage and preserve local controls during integration.
Who it puts first
Board or NRC chairInvestor or PE partnerThe referee
EVP and SVP · Architectural · 2 A4 pages
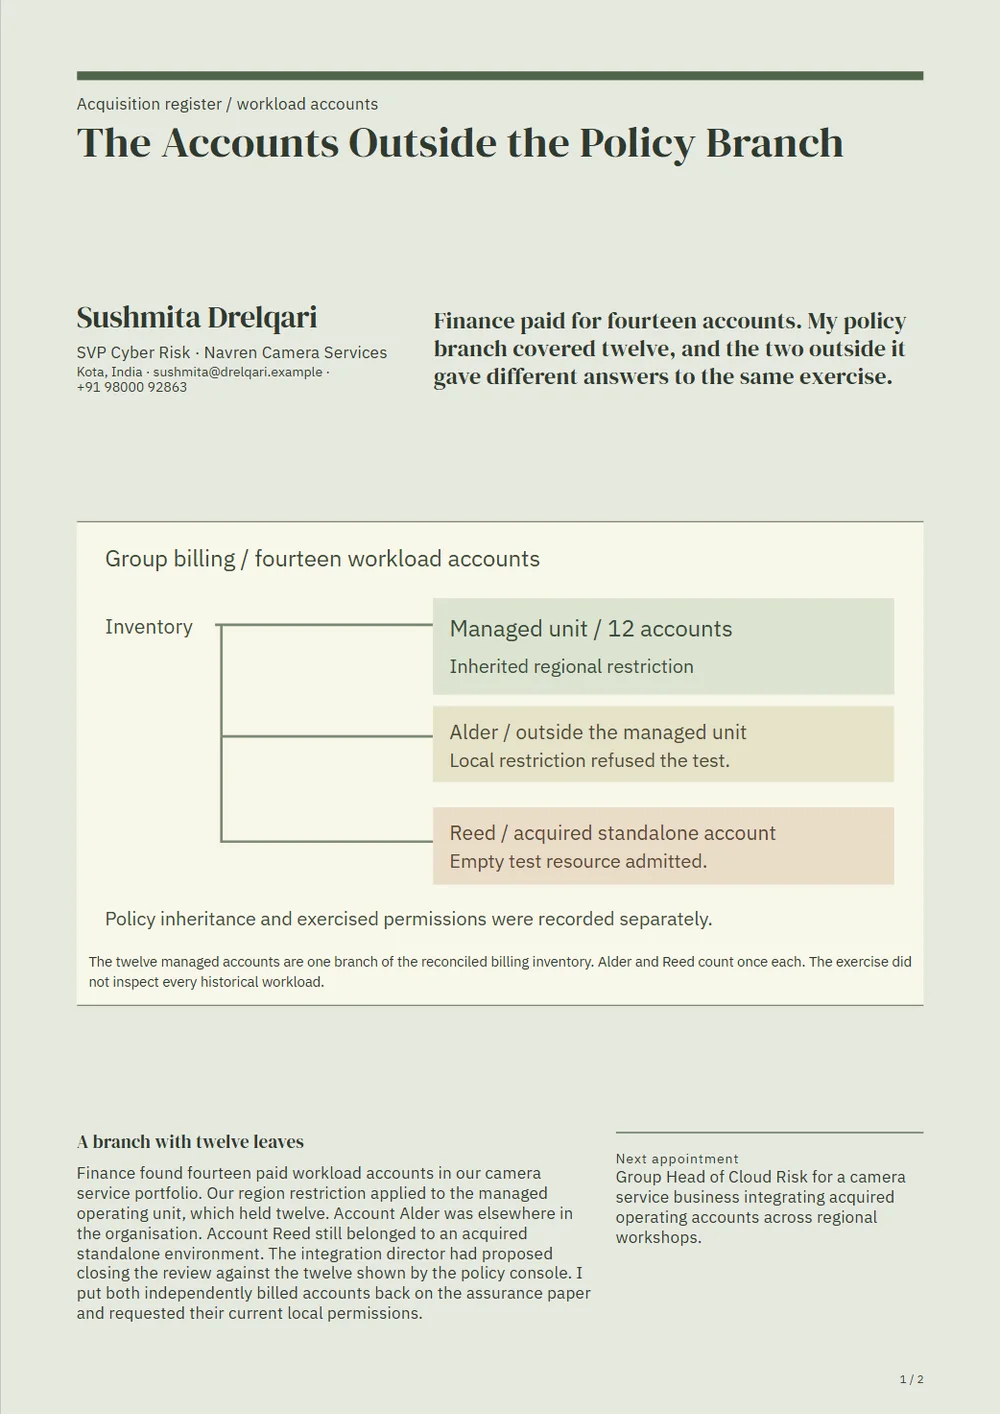
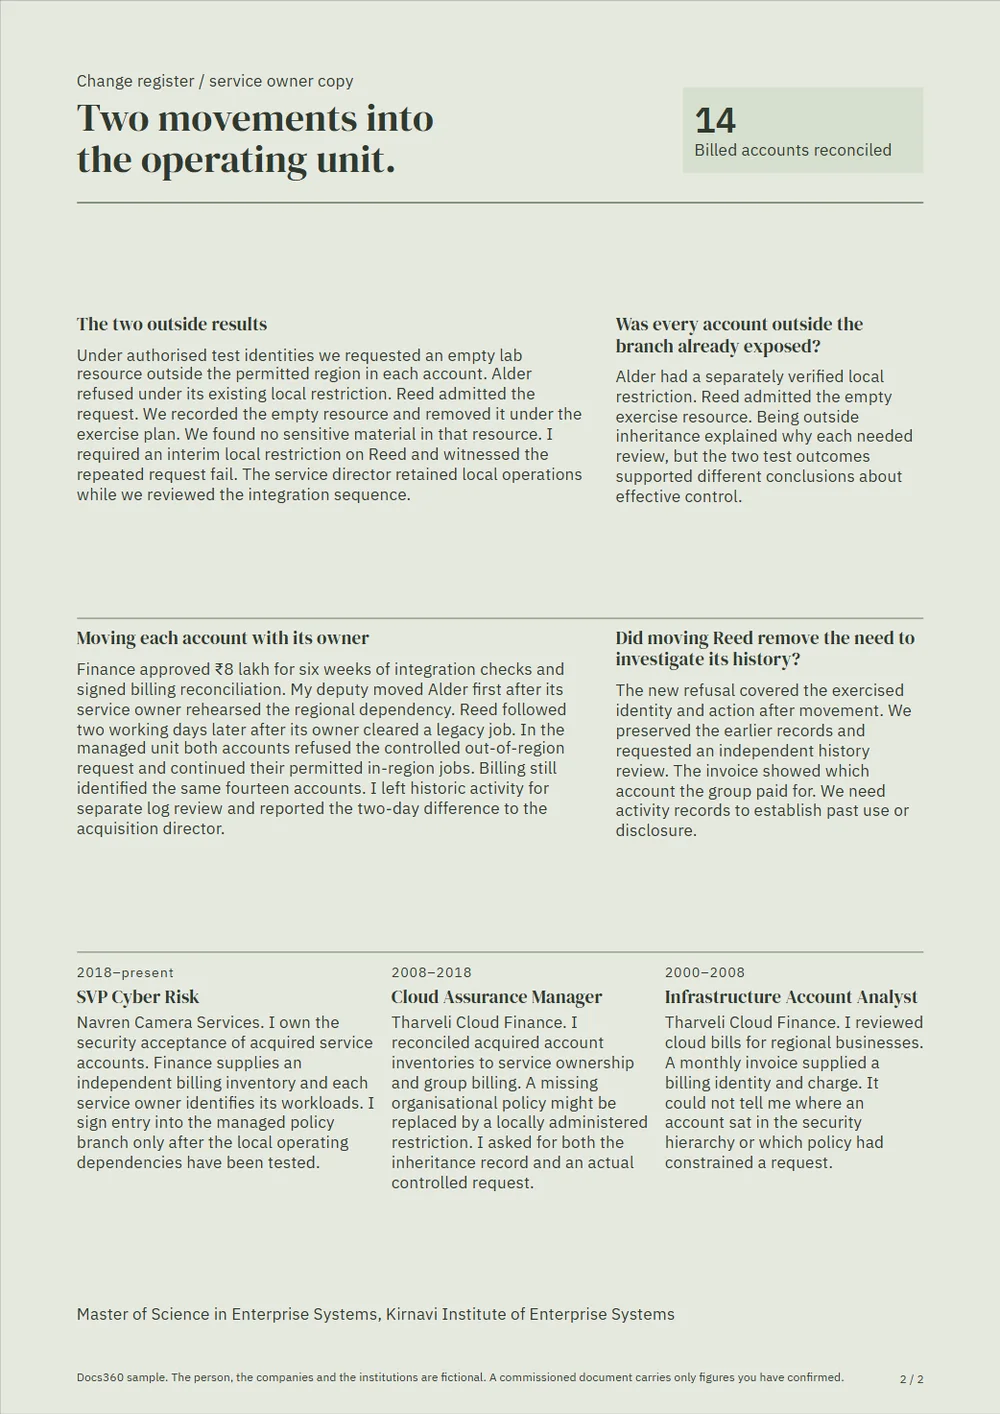
The design, and its plain companion.
The Accounts Outside the Policy Branch, as designed
2 A4 pages, printed as you see them, in real selectable text.
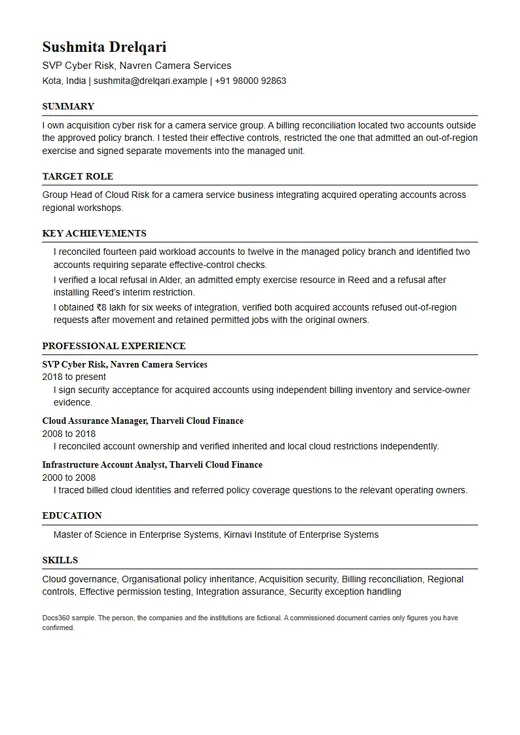
Sushmita Drelqari, the companies and the institutions on this page are fictional. A commissioned document carries only your own facts, and every figure is one you have confirmed.